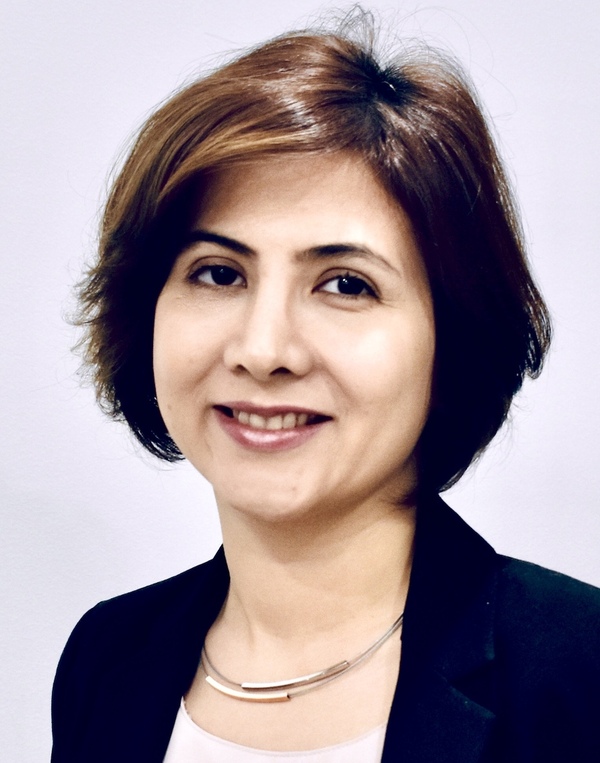
The Luvo 100
Mansooreh Zahedi
Senior Lecturer in Software Engineering
University of Melbourne
Australia
Security & Assurance
Why Mansooreh Zahedi is in the Luvo 100
Mansooreh contributes evidence about the practical barriers to making security a shared development responsibility. Co-authored research brings together published studies and practitioner discussions to identify problems with tools, roles and working practices. For developers, security specialists and operations teams, these findings offer concrete issues to address when integrating security testing into rapid software delivery.
About
Mansooreh Zahedi is Senior Lecturer in Software Engineering at the University of Melbourne, connecting empirical software engineering with DevSecOps. A co-authored review of 54 peer-reviewed studies identified 21 challenges and 31 proposed solutions for adopting DevSecOps, spanning people, practices, tools and infrastructure. The review highlighted the need for security-testing tools designed around developers’ workflows and practical ways to balance delivery speed with security.
Collaborating with Roshan Namal Rajapakse and Muhammad Ali Babar, Mansooreh also examined collaboration in application-security testing. Drawing on 48 webinars, technical talks and panel discussions, the study identified missing collaboration features in testing tools, alongside unclear roles, shared goals and ownership. It documented practices such as checking security earlier in development and outlined requirements for better tool support, giving engineering teams evidence to guide technical choices and build shared responsibility across delivery pipelines.
Career highlights
- Senior Lecturer in Software Engineering at the University of Melbourne
- Co-authored a systematic review of 54 peer-reviewed studies on DevSecOps adoption, identifying 21 challenges and 31 proposed solutions
- Co-authored an empirical study of collaborative application-security testing analysing 48 webinars, technical talks and panel discussions
- Identified critical tooling gaps and organisational friction points around shared ownership and role clarity in security testing